Madrid 3.0
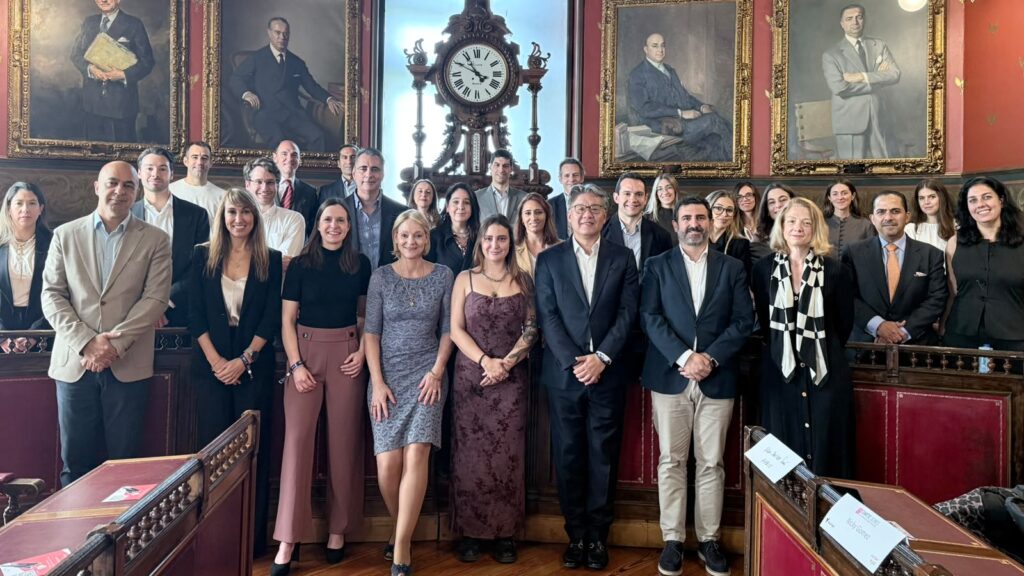
The Madrid 3.0 DARTE session took place on 27 October 2026 in collaboration with CertiK, ISBE, MERGE and MÖHRLE HAPP LUTHER. The roundtable brought together regulators, supervisors, legal practitioners and digital asset infrastructure providers to examine three points where existing EU frameworks meet crypto-asset activity: incident reporting, tax reporting and payment services.
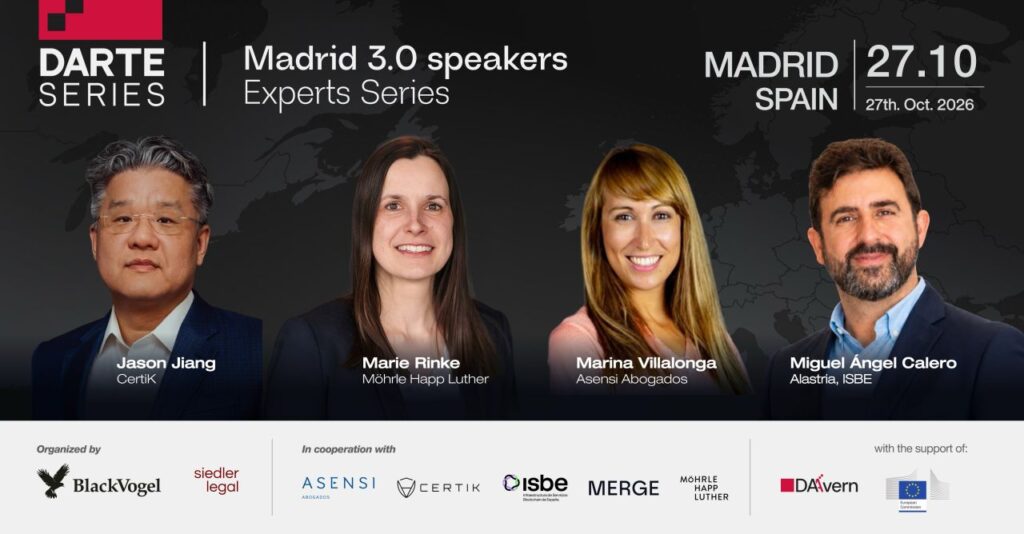
The session opened with a keynote by Miguel Ángel Calero, Executive Director of ISBE at Alastria, on three frictions that arise when regulated actors use permissionless blockchains: operational resilience, the GDPR and technological sovereignty.
Jason Jiang (CertiK) then presented on crypto-native incident classification under DORA. Marie Christin Rinke (MÖHRLE HAPP LUTHER) followed with DAC8 and standardised asset identifiers, returning to a topic the series first examined in Vienna. Marina Villalonga (Asensi Abogados) closed the technical sessions with CASP and PSP partnership models under MiCAR and PSD2/PSD3, following the discussions in São Paulo and Paris.
One theme ran through all three discussions: the cost of extending frameworks built for traditional finance onto crypto-asset activity without adapting their categories. The classifications do not map onto on-chain events. The reporting is produced and cannot be used for its stated purpose. The market is left to build compliant structures without a template from the supervisor.
The Madrid edition showed where the industry can do the groundwork itself. Participants proposed a comparative study of incident regimes, a shared asset identifier and a use-case portfolio of partnership structures, each to be aligned within the industry first and then taken to the authorities.
1 Crypto-Native Incident Classification under DORA
The first session examined how DORA’s incident regime applies to crypto-asset activity. The provisions were drafted for ICT systems under the regulated entity’s own control, and crypto produces boundary cases they do not anticipate. Affected clients are hard to define, integrity can be compromised without any downtime, block timestamps can precede the entity’s awareness, and losses are hard to quantify. Participants confirmed the problem is real but early: no reporting template has come from the regulator, and entities are pushed toward over-reporting. The discussion centred on what starts the reporting clock, with a distinction drawn between bare on-chain facts, which are public, and proprietary attribution and paid analysis, which are not.
Call to Action
- Compare the incident classification regimes of ADGM, the Hong Kong SFC, NIST and comparable frameworks, extract their minimum categories and data fields, and propose a crypto-native classification for DORA.
- Agree a common taxonomy of events between CASPs and ICT third-party providers, including providers that are not CASPs, and submit it to ESMA’s common supervisory action on custody before it concludes in 2027.
- Define the awareness trigger in layers: bare on-chain facts count as known, proprietary attribution and paid off-chain analysis do not, and the notification clock runs from detection, with root cause and loss quantification following in updates.
- Require a tamper-proof internal record of who knew what, when, and what was decided.
- Introduce a proportionate on-chain monitoring obligation for CASPs relying on smart contracts, framed as consumer protection.
- Ask analytics providers to disclose their clustering and attribution methodologies, supported by minimum quality benchmarks, and drop the call to harmonise them.
2 DAC8 and Standardised Asset Identifiers
The second session addressed the gap between what DAC8 collects and what it can achieve. A taxpayer with wallets at several CASPs is reported on by each one separately. Wrapping and bridging can appear as sales, spam tokens pollute wallet data, and the same asset is reported under different names. The tax authority receives reports that do not match, and aggregated data that cannot be used to calculate tax. The session concentrated on one proposal: a single standardised asset identifier, with the Digital Token Identifier under ISO 24165 as the existing standard. Participants also questioned the purpose and proportionality of the regime and reported a lack of crypto expertise at tax authorities. Two further proposals were deferred to a later session.
Call to Action
- Adopt one asset identifier, the Digital Token Identifier under ISO 24165, across CASPs, taxpayers and tax tooling, starting from the base asset and adding a jurisdictional layer for tokenised real-world assets and the identifier of any provider controlling a wrapped, bridged or tokenised version.
- Define standard technical event scenarios, specifying which events such as wrapping, bridging and forms of staking entail an economic change, so that national tax concepts can sit on a shared technical classification.
- Reassess DAC8 reporting against its purpose of detecting evasion and against proportionality.
- Educate the authorities through tax advisers and national associations, starting with an explanatory proposal from the associations’ tax working groups, and invite tax authorities to the next DARTE session on the topic.
- Propose refinements to ISO 24165 through the liaison between ISO/TC 68 and ISO/TC 307, and examine registry alternatives to a single provider.
- Schedule a dedicated follow-up session for the two deferred proposals.
3 CASP and PSP Partnership Models under MiCAR and PSD2/PSD3
The third session asked a practical question: how does a CASP that needs a payment authorisation for e-money token services structure a partnership with a payment service provider? Five structures were set out: agent, outsourcing, distribution, white-label and hybrid or intra-group models. Each allocates risk and obligations differently. Open questions remain on strong customer authentication, safeguarding, and the triangular passport problem across three Member States. Participants mapped diverging supervisory practice across jurisdictions and noted that mandatory rules limit what a contract can shift between the parties. The session converged on a pragmatic reading: a partnership is a time-to-market solution and a learning period before the CASP obtains its own licence.
Call to Action
- Build a use-case portfolio of real agent, outsourcing, distribution, white-label and intra-group arrangements, covering risk allocation, client contracting, service levels and the supervisory response, as the alternative to prescriptive guidelines.
- Obtain clarity from the EBA and ESMA on the trigger: when activities involving e-money tokens, including trading against a stablecoin and settlement to a third-party custodian, constitute a payment service.
- Streamline joint applications where the overlap is foreseeable, processing a limited payment institution application alongside the CASP application, with a memorandum of understanding where supervisors are separate.
- Clarify at legislative level whether own-funds requirements under MiCAR and the payments framework may be counted jointly within a single entity.
- Treat partnership as an interim structure with a defined path to an own licence, and align within the industry before submitting Q&A questions to the authorities.
Madrid 3.0 PARTNERS

For more information about the MiCAR Roundtable Expert Series:
info@blackvogel.com / nina.siedler@siedler.legal