London 3.0
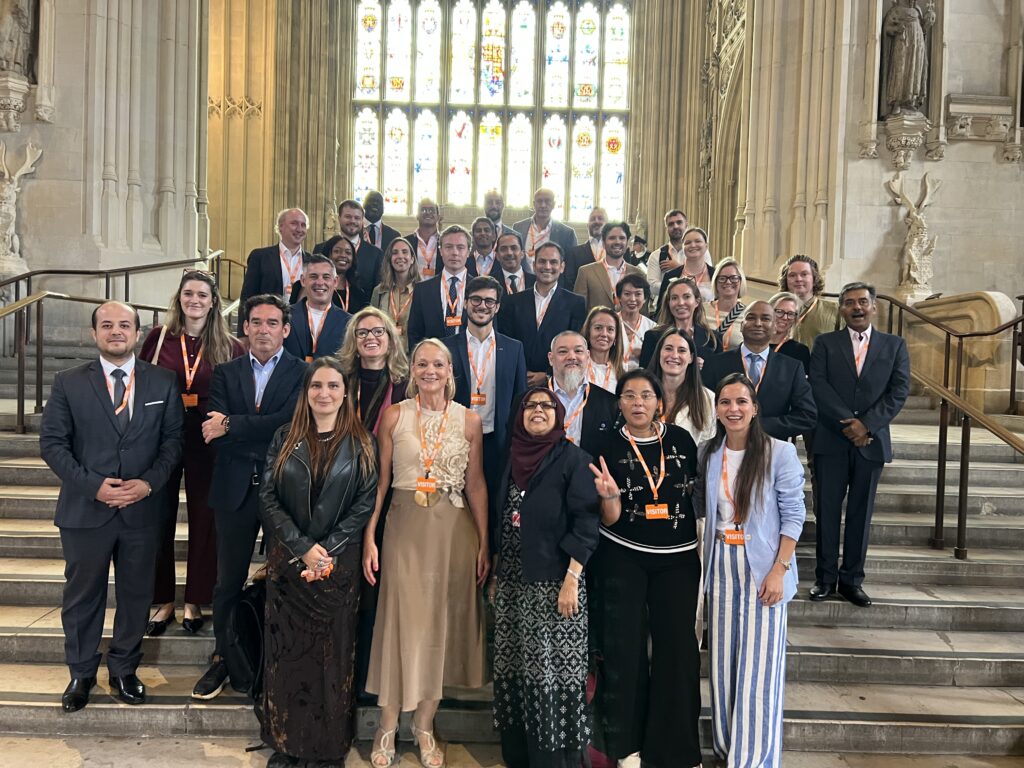
The London 3.0 DARTE session took place on September 7th, 2026, at the House of Lords, in collaboration with the Blockchain Game Alliance, DAAvern, and the Institute of Free Technology, and with the support of the European Commission. This edition departed from the usual structure of DARTE sessions, concentrating on a single question rather than three: whether financial confidentiality is a precondition of property rights and competitive markets, and what follows if it is.
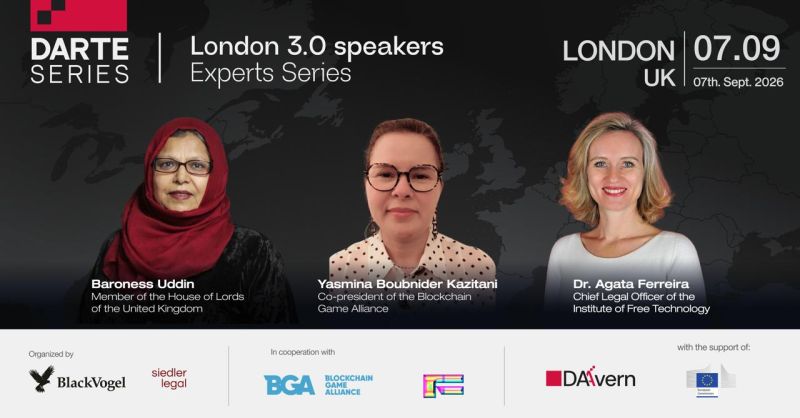
The session opened with welcome notes by Baroness Uddin and Yasmina Kazitani, followed by an introduction to the DARTE concept by Mariana de la Roche Wills (BlackVogel). Dr. Agata Ferreira (Institute of Free Technology) then set out the historical position, in which lawful financial affairs were presumed confidential and disclosure required a specific reason, and traced how four decades of successive disclosure regimes inverted that presumption. Public distributed ledgers are the end point of that trajectory: the first financial system in which total, permanent, global exposure is the default rather than the exception. The discussion that followed was cross-cutting, examining the consequences for property rights and personal security, for market integrity and competition, and for the neutrality of the infrastructure itself. The session concluded with closing remarks by Dr. Nina-Luisa Siedler (siedler legal and DAAvern).
The analytical move that shaped the discussion was to stop treating privacy as one thing. Much of the apparent conflict between confidentiality and supervision dissolves once two distinctions are drawn: between the layers of the technology stack, and between the different things the word privacy describes. Data protection law addresses those who determine how personal data is processed. Financial regulation addresses intermediaries at the point of their interaction with customers. Neither requires the underlying infrastructure to be public.
The London edition reinforced DARTE’s role as a venue where a contested position can be tested rather than asserted. Participants with direct supervisory and compliance responsibility put the case for the existing controls, and the session did not reach consensus on every point. What it did establish is that the current framing, which treats exposure as transparency and confidentiality as concealment, is not the only available one, and that the precedent of encryption suggests how the question has been resolved before.
1 Confidentiality as a Component of the Property Right
The first strand examined what it means that digital assets are now recognised as objects of proprietary rights across a growing number of legal systems, while that recognition stays silent on control over information about the asset. In established categories of property, the right to exclude the general public from knowledge of the property forms part of the right itself. On a public ledger no such control exists from the moment the asset is issued, and information that would be protected as undisclosed commercial information in any other setting, including trading positions, counterparties, treasury operations, and settlement patterns, is exposed to everyone, including competitors, permanently and at no cost. Participants emphasised that this is a security question as much as a privacy one, since the same data is the input for address spoofing, extortion, and the documented rise in violent robbery of individuals targeted because their holdings are visible. The problem extends past financial information to voting, membership, credentials, and identity registers held on distributed ledgers.
Call to Action
- Recognise that holders have a protectable interest in information about the asset, and address the question directly through international harmonisation projects and national law reform commissions.
- Make confidentiality of ledger information the default, with disclosure defined for specific circumstances, to a counterparty, a supervisor, an auditor, or a court, rather than to everyone by default.
- Assess exposure against the established proportionality tests. Is it necessary to a legitimate objective, is it the least intrusive means available, and is generalised permanent publication proportionate where targeted disclosure would serve?
- Treat confidentiality as a design requirement where ledger records engage civic and non-financial interests, including voting, association, and credentials.
2 Transparency as a Market Integrity and Competition Problem
The second strand examined the consequences of publishing transaction data in markets that depend on not publishing it. Because instructions are visible before they take effect, an observer can trade ahead of them, position around them, or reorder them for gain. In regulated markets that conduct is front-running and a breach of the duty to act in the client’s best interests; in tokenised markets it has been an accepted business model with published tooling and measurable revenue. Participants noted that regulated markets do not police front-running primarily through enforcement, they prevent it by not publishing the orders in the first place. The competition effect is already visible, with serious transaction volume routing around public channels at additional cost and institutional platforms built confidential by default. A third consequence concerns the operators of the infrastructure rather than its users: operators who can be identified can be pressured, and the routing of Ethereum blocks through sanctions-compliant relays following the Tornado Cash designations showed how quickly shared infrastructure becomes selective once its operators are visible.
Call to Action
- Support technical solutions that do not broadcast instructions before execution, and the routing of transaction orders through confidential channels. An order that is not published cannot be traded ahead of.
- Treat confidentiality of the ledger as a design requirement and disclosure as the regulated exception, which is the architecture the rest of financial markets already use.
- Recognise confidentiality as a property of the neutrality and operational resilience of market infrastructure, and treat measures protecting the privacy of technical operators as resilience measures.
3 Verifiability over Exposure: Supervision without Mass Collection
The third strand addressed the framing of the debate itself. The choice is routinely presented as all or nothing, either everything is public or enforcement is blind, and that framing conflates confidentiality with opacity. Confidentiality is selective disclosure and control, where different actors see different things according to their entitlement, which is how financial supervision already operates. Participants observed that mass data collection does not remove exposure, it moves it, recreating the same problem in centralised intermediary, vendor, and analytics databases that the people recorded in them cannot inspect and that are themselves targets. Two practical obstacles were identified. Privacy technologies are treated as a single undifferentiated class, so tools that let a supervisor verify a specific fact without seeing anything else are regulated as though they offered blanket anonymity. And selective disclosure has no regulatory recognition and no evidentiary standard, with competing methods offering different guarantees and no common standard between them. Transport encryption took the opposite route: it became a standard first, then interoperable, and regulatory recognition followed
Call to Action
- Align the standard with how financial markets already operate: targeted disclosure to those entitled to it, with the obligation concentrated on regulated intermediaries and the records they handle, and the infrastructure ledger confidential by default.
- Confirm, at supervisory and standard-setting level, that the use of privacy-preserving technology is not of itself a high-risk indicator where an institution can evidence equivalent or better outcomes, consistent with the risk-based approach those standards already rest on.
- Issue guidance clarifying that legitimate disclosure is circumstance-specific, triggered by a defined event or lawful request, held by the party that owes the duty, and limited to the fact required.
- Establish a joint supervisor and industry group to define minimum evidentiary verifiability artefacts, narrow and configurable in scope, with industry guidance as the practical outcome.
- Remove the obstacles to developing privacy-preserving technology, including the exposure of developers to liability for the act of building it.
London 3.0 PARTNERS

For more information about the MiCAR Roundtable Expert Series:
mariana@delaroche.consulting / nina.siedler@siedler.legal